Qilin Ransomware
- 128
- Global rank
- 109
- Month rank
- 67
- Week rank
Qilin ransomware (predecessor known as “Agenda”) is a rapidly evolving ransomware-as-a-service (RaaS) operation targeting organizations worldwide. Known for double extortion tactics (encrypting files while also threatening to leak stolen data) Qilin has quickly gained notoriety for its customization, flexibility, and impact on critical infrastructure.
- Ransomware
- Type
- Unknown
- Origin
- 1 July, 2022
- First seen
- 15 October, 2026
- Last seen
How to analyze Qilin Ransomware with ANY.RUN
IOCs
IP addresses
- 48.209.6.48
- 23.11.40.157
- 74.179.77.204
- 2.23.246.101
- 135.232.92.97
- 2.16.204.158
- 23.207.210.139
- 131.253.33.203
- 20.190.160.5
- 48.192.1.64
- 150.171.109.105
- 23.59.18.102
- 2.16.204.155
- 172.211.123.250
- 172.211.123.248
- 48.192.1.65
- 92.123.104.62
- 162.159.142.9
- 40.126.32.136
- 2.21.239.162
Hashes
- 04f0f2652d02478a9f2dc10692ffe3f210e63b4376b219f486dabf75e8a06241
- ce79427811c1cc7ca2078f313356c348155c4b709f24c24fd0c05e20ccc5a5d0
- f49b515eedeed1abe391bc32f15ce43d3582cb6c41ff944fa9c79f476d5824ba
- 025daab85887f5f7e52a9f7cc37701bef57513478fda5f8d5763f9ccd896e940
- 5623087c5bd28f8f93c2d64c054e685306894032eb3b0f95794efca89b0b73cf
- 5f4afc766685e909e0c6803d916a2605f8b0db1975d0a442fcb0a1682ad52e12
- 3db4cd30fa85d28ea51d636349e36b4e32098b871ef249d8a70dec1b3950ebaf
- 61f7aa918b55238278a1666cb723df9e3639d229d1027611e02ae3808ede33ed
- 95da81f80b3971082e6a369d69bab9f30a507a233a353c29a29b90fe61f09ffb
- d9e82680968224932ad5d76a8d8c7924f4ee909bed72d74c7e42693f5f039048
- 15249d8fcd6c59755622790123259c8a06a0a10d8ce4de66e394609cef2abb2b
- f910b2a6d84d0677cda9aefabfa4a45863ba51a8831588e3b527e8e1d3a9927c
- 2604d1677a34ef72d754d7051bd759aa1e9bd7010e07dc9acefa51b4c2e8f4a5
- bf6b53c615346c5419d6661287d7913b1d2d6ed862c5e9e1e6b5eeb670973c9f
- 741d42058a5c714e801f0dd2fa83331ea00dfd6b775689c1a623bc6ebafba240
- 6d05e1ad492aeda1e02c6f75e507f57874d9a5eed8d9e8a0a01cdfcb1bdf5289
- 7ce1b0525cecf639a75b2ab421207025c80600bfda07eed090e3c98b224563e1
- eff52743773eb550fcc6ce3efc37c85724502233b6b002a35496d828bd7b280a
- 89f2a5c6be1e70b3d895318fdd618506b8c0e9a63b6a1a4055dff4abdc89f18a
- 93ff42e60c442559119478cca468b190bade2b030e638788c4400c01f5336958
Domains
- www.microsoft.com
- settings-win.data.microsoft.com
- client.wns.windows.com
- ecs.office.com
- google.com
- fe3cr.delivery.mp.microsoft.com
- th.bing.com
- ocsp.digicert.com
- activation-v2.sls.microsoft.com
- slscr.update.microsoft.com
- crl.microsoft.com
- login.live.com
- oneocsp.microsoft.com
- nexusrules.officeapps.live.com
- self.events.data.microsoft.com
- brought-cup-formation-projects.trycloudflare.com
- go.microsoft.com
- www.bing.com
- omex.cdn.office.net
- odc.officeapps.live.com
URLs
- http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
- http://www.microsoft.com/pkiops/crl/microsoft%20secure%20server%20ca%202026.crl
- http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbtrjrydryt%2bapf3gspypfhbxr5xtqqus9tippmhxdiunkhmewnpyim8s8yceajtxtab8my1oj8mfwpz%2f7y%3d
- http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
- http://oneocsp.microsoft.com/ocsp/mfqwujbqme4wtdajbgurdgmcgguabbq3l3%2f%2fa6adk8nray2gxzvayrhg4aqub6t%2b2v%2bxq3lso2d33ojhnyhhqoucezmaaaafuwohyjguzpcaaaaaaau%3d
- https://login.live.com/rst2.srf
- https://login.live.com/ppsecure/deviceaddcredential.srf
- https://th.bing.com/th?id=odswg.iotdlocalicon&w=16&h=16&c=1&rs=1&p=0
- http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20update%20secure%20server%20ca%202.1.crl
- https://slscr.update.microsoft.com/sls/%7b522d76a4-93e1-47f8-b8ce-07c937ad1a1e%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
- https://fe3cr.delivery.mp.microsoft.com/clientwebservice/ping
- https://slscr.update.microsoft.com/sls/ping
- https://slscr.update.microsoft.com/sls/%7be7a50285-d08d-499d-9ff8-180fdc2332bc%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
- https://activation-v2.sls.microsoft.com/slactivateproduct/slactivateproduct.asmx?configextension=retail
- https://settings-win.data.microsoft.com/settings/v3.0/wsd/waasassessment?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&ring=retail&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=bad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=10.0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=waasassessment&processorcores=6¤tbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&servicingbranch=cb&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&honorwufbdeferrals=0&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
- https://settings-win.data.microsoft.com/settings/v3.0/wsd/waasassessment?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&ring=retail&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=bad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=10.0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=waasassessment&processorcores=6¤tbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&servicingbranch=cb&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&honorwufbdeferrals=1&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
- https://settings-win.data.microsoft.com/settings/v3.0/flightsettings/fsservice?processorclockspeed=3094&isretailos=1&oemmanufacturername=dell&flightingpolicyvalue=3&enablepreviewbuilds=4294967295&osversionfull=10.0.19045.4046.amd64fre.vb_release.191206-1406&managepreviewbuilds=3&branchreadinesslevelsource=0&attrdataver=186&processorcores=6&branchreadinesslevelraw=16&totalphysicalram=6144&tpmversion=0&oemmodelnumber=dell&systemvolumetotalcapacity=260281&deviceid=s%3abad99146-31d3-4ec6-a1a4-be76f32ba5d4&app=fss&appver=10.0&smartactivehoursstate=1&activehoursstart=20&securebootcapable=0&activehoursend=13&devicefamily=windows.desktop
- https://www.bing.com/dsb/search?dsbmr=1&format=dsbjson&client=windowsminiserp&dsbschemaversion=1.1&dsbminiserp=1&q=q&cc=us&setlang=en-us&clientdatetime=10%2f12%2f2026%2c%209%3a51%3a03%20pm
- https://www.bing.com/threshold/xls.aspx?t=5&dl=1&f=9&wsbc=1
- https://www.bing.com/th?id=odswg.d1ba30db-6e28-43b2-8ccf-6541816547ed&pid=dsb
Last seen at
- 04f0f2652d02478a9f2dc10692ffe3f210e63b4376b219f486dabf75e8a06241.bin.gz
- 61f7aa918b55238278a1666cb723df9e3639d229d1027611e02ae3808ede33ed.exe
- 15249d8fcd6c59755622790123259c8a06a0a10d8ce4de66e394609cef2abb2b.elf
- qilin.zip
- qilin.zip
- 907c48316ea3d9592204cc16c817530b7bdaeed7f04d32535dac66de3713202c.zip.zip
- 907c48316ea3d9592204cc16c817530b7bdaeed7f04d32535dac66de3713202c.zip
- 907c48316ea3d9592204cc16c817530b7bdaeed7f04d32535dac66de3713202c.zip.zip
- 907c48316ea3d9592204cc16c817530b7bdaeed7f04d32535dac66de3713202c.zip
- 61f7aa918b55238278a1666cb723df9e3639d229d1027611e02ae3808ede33ed.zip
What is Qilin Ransomware?
Qilin operates as a Ransomware-as-a-Service (RaaS) platform, providing criminal affiliates with sophisticated tools and infrastructure to conduct ransomware attacks. Gained popularity by late 2023 and has since become increasingly sophisticated in its operations. Amassed over $50 million in ransom payments in 2024 alone. Ranked as the most prevalent ransomware in public threat intelligence reports by 2025.
Last year, cybersecurity company Halcyon discovered an improved version of the ransomware that it named Qilin.B. This newer variant demonstrates enhanced capabilities in terms of encryption speed, evasion techniques, and payload delivery mechanisms.
What sets Qilin apart from other ransomware families is its focus on operational efficiency and stealth. Once Qilin has gained initial access, it employs advanced obfuscation techniques to evade detection. The ransomware code is packed, disguising its true nature to avoid static analysis.
The group has also demonstrated remarkable adaptability, quickly capitalizing on disruptions to competing ransomware operations to expand their affiliate base and market presence.
Qilin is written in Rust and Go, enabling cross-platform attacks against both Windows and Linux environments. Qilin’s modular design allows attackers to customize payloads, set encryption methods, and configure ransom notes. The ransomware has a professionalized infrastructure, including a data leak site where stolen information is published if victims refuse to pay.
Qilin Malware Victimology
Qilin targets a diverse range of organizations across multiple sectors, with a particular focus on high-value targets that are likely to pay substantial ransoms. In June 2025, the United States remained the primary target of ransomware attacks, recording 235 victims, far surpassing other nations. Canada (24), the United Kingdom (24), Germany (15), and Israel (13) also experienced notable activity.
The threat actors behind Qilin demonstrate a clear preference for:
- Healthcare Organizations: Hospitals and medical facilities are frequent targets due to their critical nature and limited tolerance for downtime -Financial Services: Qilin Ransomware Attack hit a U.S. financial advisory firm on July 1, 2025. The attackers allegedly exfiltrated approximately 340 GB of sensitive data, potentially including confidential financial records, client information, and internal communications. -Manufacturing and Industrial Facilities: Critical infrastructure targets that cannot afford extended operational disruptions -Educational Institutions: Universities and school districts with valuable research data and personal information -Government Agencies: Local and regional government entities with sensitive citizen data -Professional Services: Law firms, consulting companies, and other service providers handling confidential client information
The targeting strategy appears to prioritize organizations in developed economies where cyber insurance coverage is common and ransom payment capabilities are higher. The geographical distribution reflects this focus, with North America and Europe representing the majority of victims.
Qilin Ransomware Attack Chain and Technical Details
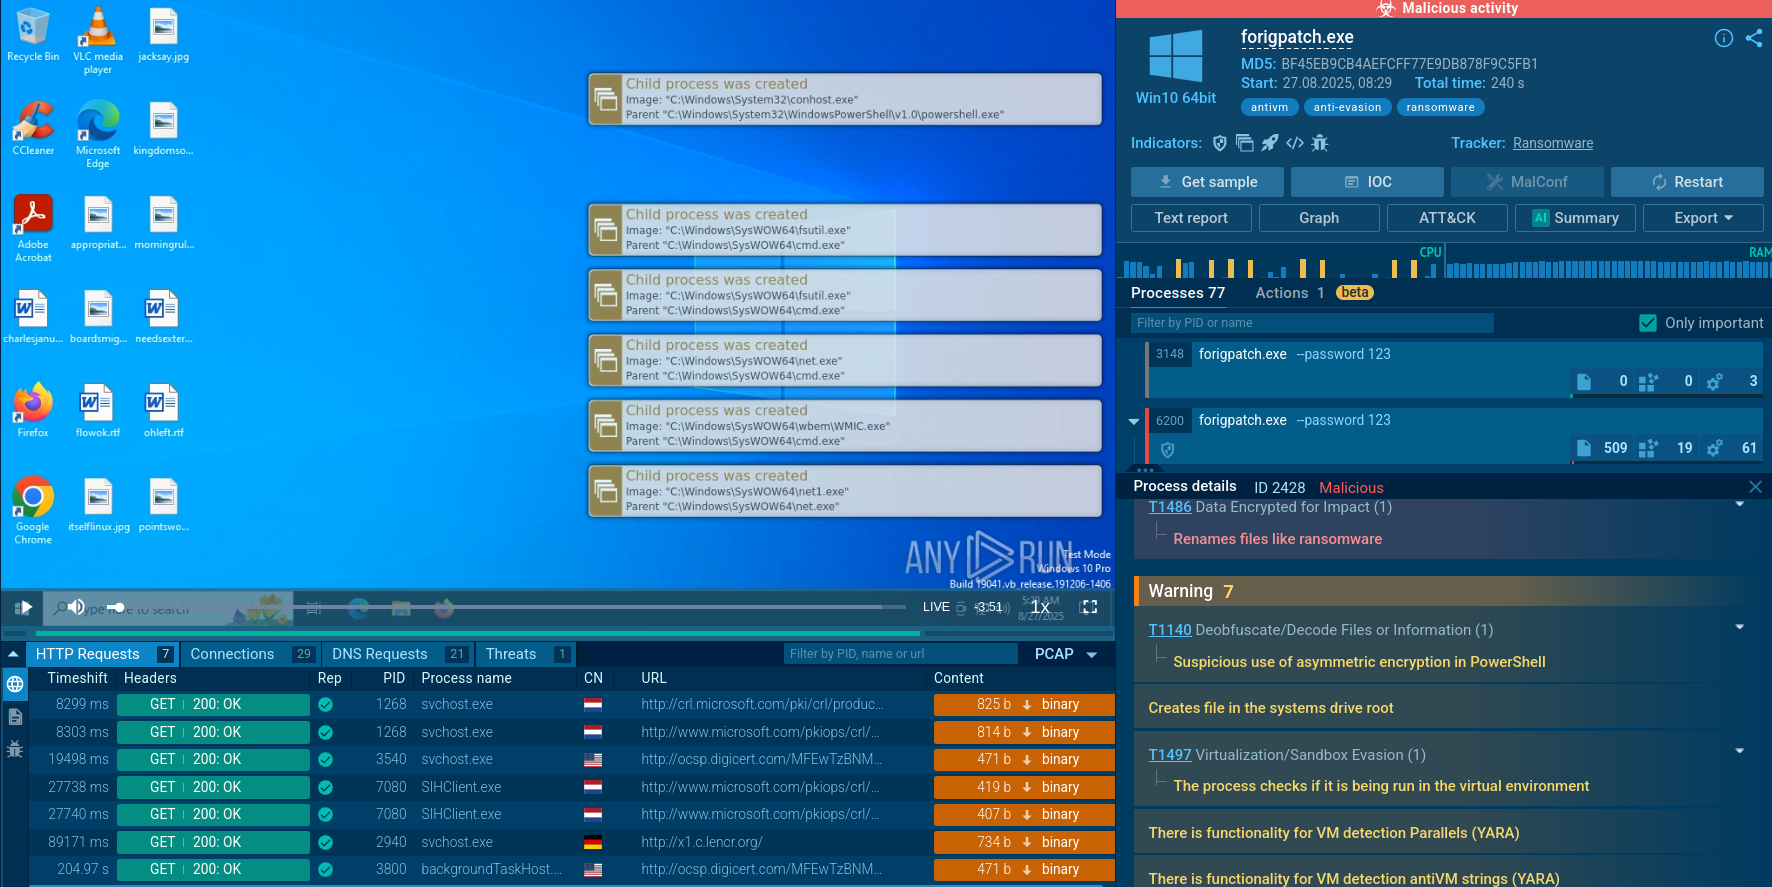
One of Qilin’s features is the requirement to input a unique password, passed as a command-line argument when launching the executable file, which enhances its protection against analysis.
The community of about half a million users of ANY.RUN’s Interactive Sandbox has submitted and analyzed a number of Qilin’s samples featuring this password input. Let’s view an analysis with a correctly entered password.
View Qilin detonated in the Sandbox
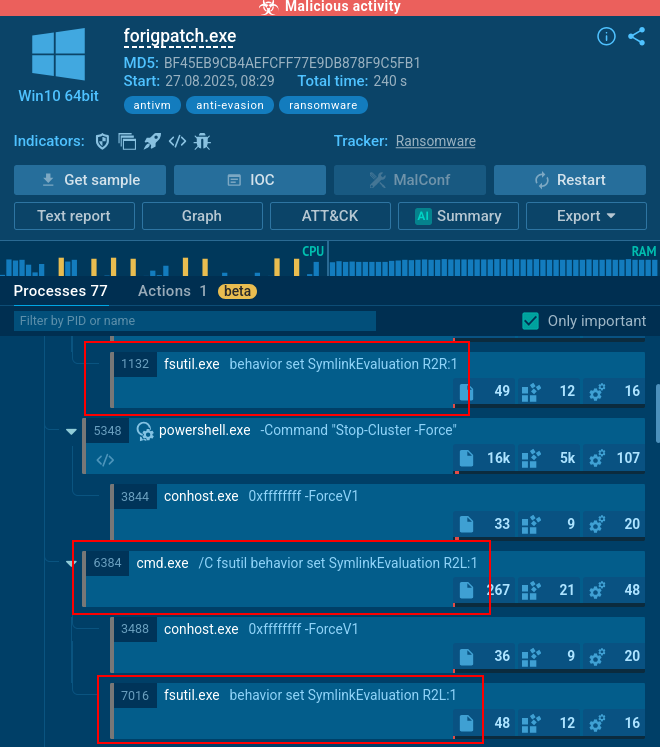
Qilin employs commands to manipulate symbolic links in Windows, altering the system's behavior regarding the handling of symbolic links. The commands used are:
fsutil behavior set SymlinkEvaluation R2R:1
fsutil behavior set SymlinkEvaluation R2L:1
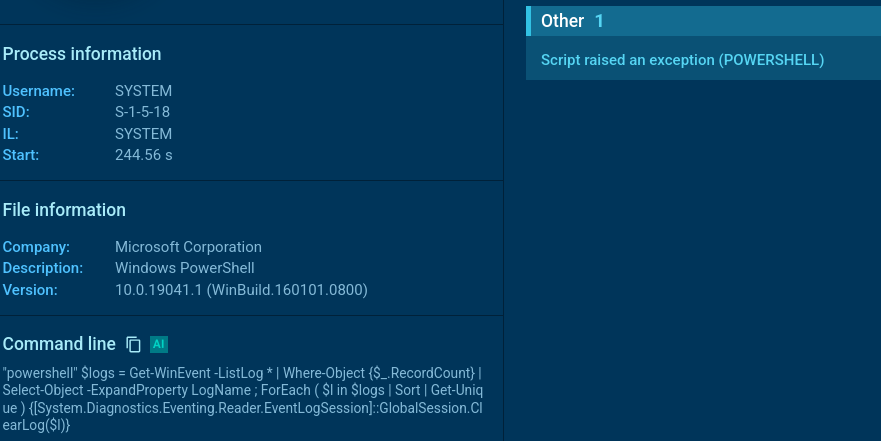
To conceal the traces of its activity, Qilin clears system logs, making it difficult to detect and analyze the attack, using a PowerShell script:
Subsequently, the malware destroys Volume Shadow Copies (VSS) to prevent data recovery without paying the ransom. To do this, the ransomware executes a sequence of commands that manipulate the Volume Shadow Copy Service and deletes all existing snapshots. The commands used are:
net start vss wmic service where name='vss' call ChangeStartMode Manual vssadmin.exe delete shadows /all /quiet net stop vss wmic service where name='vss' call ChangeStartMode Disabled
Qilin also uses commands to prevent failures in cluster services and to propagate through a domain environment via Active Directory (AD). These commands include:
Stop-Cluster -Force
Import-Module ActiveDirectory ; Get-ADComputer -Filter * | Select-Object -ExpandProperty DNSHostName
ServerManagerCmd.exe -i RSAT-AD-PowerShell ; Install-WindowsFeature RSAT-AD-PowerShell ; Add-WindowsCapability -Online -Name 'RSAT.ActiveDirectory.DS-LDS.Tools~~~~0.0.1.0'
Qilin encrypts files, appending an extension composed of a unique set of random characters for each attack. This extension is also included in the name of the ransom note file left in the infected directories.
How Qilin Ransomware Generally Functions
Qilin operates through a sophisticated technical architecture designed for maximum effectiveness and stealth. Adversaries operating the Qilin ransomware adopt a multi-pronged strategy to breach target networks, relying on both misconfigurations and software vulnerabilities.
Common Entry Points:
- Vulnerability exploitation
- Exploitation of unpatched VPN appliances and firewalls
- Compromise of Remote Desktop Protocol (RDP) services
- Phishing campaigns targeting employee credentials
- Supply chain compromises through trusted vendor access
- Exploitation of public-facing web applications
- Abuse of legitimate remote access tools
Lateral Movement Techniques:
- Once inside a network, Qilin employs various techniques to spread:
- Credential dumping from compromised systems
- Pass-the-hash and pass-the-ticket attacks
- Exploitation of Windows vulnerabilities for privilege escalation
- Living-off-the-land techniques using legitimate system tools
- Network scanning to identify additional targets
- Abuse of administrative tools like PowerShell and WMI
Network Persistence:
- Creation of backdoor accounts and hidden administrative access
- Installation of remote access tools for persistent connectivity
- Modification of security policies to maintain access
- Deployment of additional payloads for redundant access
Advanced Evasion Techniques:
Further, Qilin uses various code obfuscation methods, such as renaming functions, altering control flows, and encrypting strings, to complicate reverse engineering efforts. This also makes Qilin difficult to detect with IOCs located further along the killchain.
Anti-Analysis Mechanisms:
To further hinder analysis, Qilin integrates anti-analysis mechanisms designed to identify and disable debugging and sandbox environments. It actively scans for virtual machines and common sandbox artifacts to evade dynamic analysis, preventing security researchers from closely examining its behavior.
Encryption Implementation:
The ransomware implements robust encryption algorithms with the following characteristics:
- Uses industry-standard AES-256 encryption for file encryption
- Employs RSA public-key cryptography for key protection
- Generates unique encryption keys for each infected system
- Implements secure key management to prevent unauthorized decryption
Communication Infrastructure:
- Utilizes Tor networks for command and control communications
- Implements secure communication protocols to protect operator anonymity
- Maintains redundant infrastructure to ensure operational continuity
- Uses cryptocurrency payment systems for ransom collection
What Qilin Malware Can Do to an Endpoint Device
When Qilin successfully infiltrates a device, it implements a multi-stage attack process designed to maximize damage while evading detection:
Initial Compromise and Persistence:
- Establishes persistence mechanisms through registry modifications and scheduled tasks
- Creates backup access points to maintain access even if primary entry vectors are discovered
- Disables Windows Defender and other security solutions through privilege escalation
System Manipulation:
Using renamed binaries like upd.exe (a spoof of legitimate AV updaters), Qilin ransomware disables EDR, clears logs, and bypasses detection. The malware might even exploit outdated Carbon Black Cloud sensors to remain hidden.
Credential Harvesting:
Once elevated, Qilin dumps LSASS memory and extracts credentials to facilitate lateral movement across the network. This process allows the ransomware to escalate privileges and access additional systems.
Data Encryption Process:
- Encrypts files using strong cryptographic algorithms, typically AES-256 with RSA key protection
- Targets specific file types while avoiding system files necessary for basic OS functionality
- Appends custom file extensions to encrypted files
- Drops ransom notes in multiple locations across the infected system
- Modifies desktop wallpaper to display ransom information
System Degradation:
- Disables system recovery features including Windows System Restore
- Deletes shadow copies and backup files to prevent easy recovery
- Clears event logs to hinder forensic analysis
- May corrupt or delete system files to increase recovery complexity.
Notable Qilin Attacks
The scope of Qilin's operations has grown dramatically. investigated network artifacts related to Qilin and identified three probable cases of the ransomware across the Darktrace customer base between June 2022 and May 2024. However, by 2025, the frequency had increased exponentially, with the group claiming dozens of victims monthly.
A Qilin Ransomware Attack hit a U.S. financial advisory firm on July 1, 2025. The attackers allegedly exfiltrated approximately 340 GB of sensitive data, potentially including confidential financial records, client information, and internal communications. This incident underscores the persistent threat Qilin poses to financial services organizations.
The Qilin ransomware group launched attacks exploiting Fortinet vulnerabilities CVE-2024-21762 and CVE-2024-55591 between May and June 2025. These attacks demonstrated Qilin's ability to target critical infrastructure through systematic exploitation of network security appliances.
Multiple healthcare organizations have fallen victim to Qilin attacks, resulting in cancelled surgeries, delayed medical procedures, and compromised patient care. These attacks highlight the life-threatening potential of ransomware when targeting critical infrastructure.
Several universities and school districts have been targeted, resulting in exposure of student records, research data, and administrative systems. These attacks often occur during critical periods such as registration or examination periods to maximize pressure for ransom payment.
Gathering Threat Intelligence on Qilin Ransomware
Effectively countering such complex threats as Qilin is impossible without access to a large volume of detailed up-to-date threat Intelligence. It fuels:
- Proactive detection based on studying the malware's behavior before it attacks corporate systems.
- Creating High-Quality Signatures and Correlation Rules: Understanding specific commands, scripts, and sequences of actions enables the configuration of security systems (SIEM, EDR) for precise attack detection.
- Investigating Incidents: TI data helps analysts quickly understand the scope and methods of an attack, identify affected systems, and take appropriate response actions.
Indicators of Compromise (IOCs) include:
- Presence of unusual Rust/Go executables.
- Suspicious processes terminating backups or security tools.
- Encrypted files with unique extensions set by affiliates.
- Outbound connections to Tor-based C2 servers.
- Ransom notes dropped across multiple directories.
Behavioral detection (via EDR/XDR) is critical: look for privilege escalation, mass file encryption, and registry tampering.
Start using Threat Intelligence Lookup for free: collect IOCs, browse sandbox detonations.
Start with a malware name search request to ANY.RUN’s Threat Intelligence Lookup and dive deeper into contextual data on Qilin. View public analyses of the malware’s fresh samples, extract the behavioral patterns, gather IOCs from each session.
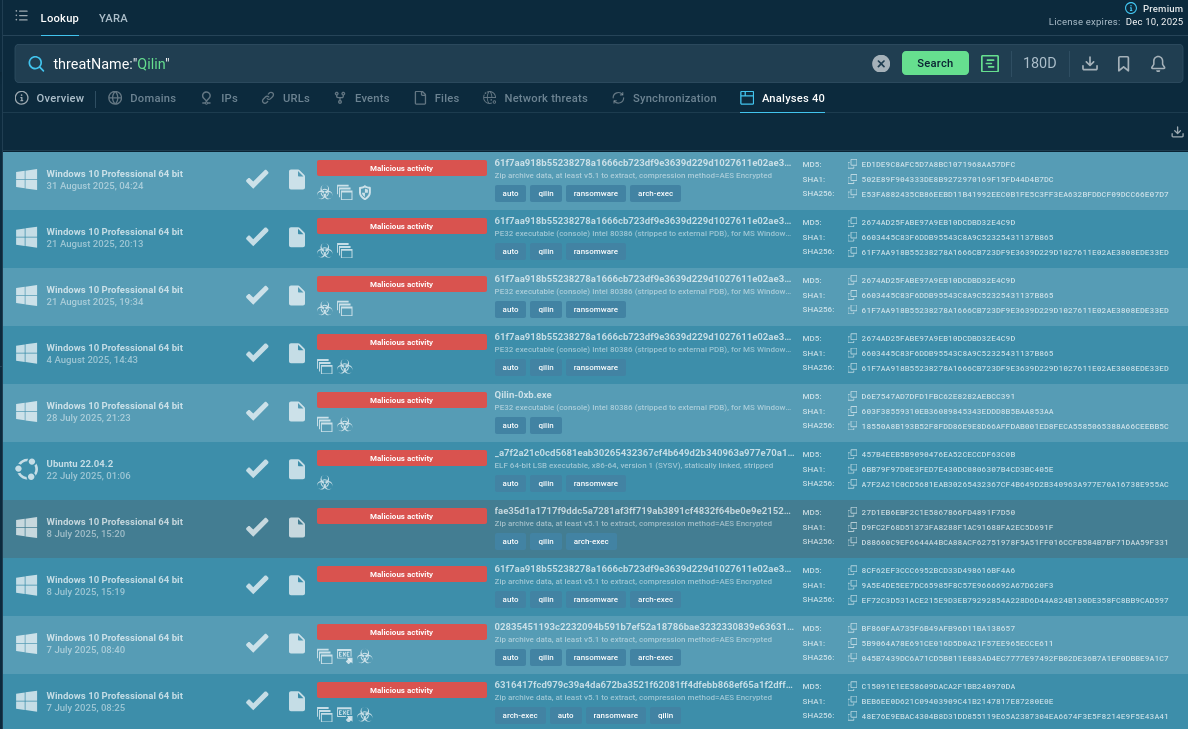
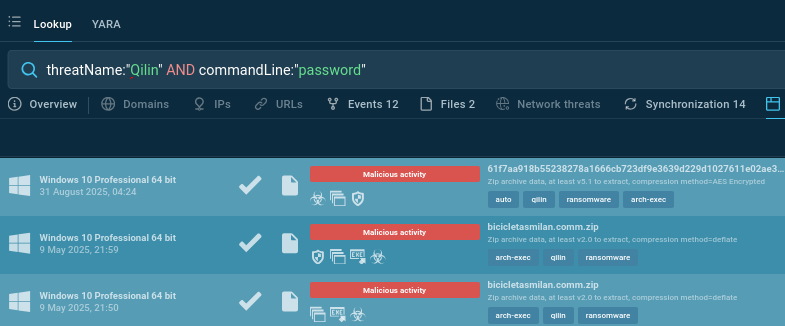
To find Qilin samples with the above-mentioned password submitting, use an additional search parameter:
threatName:"Qilin" and commandLine:"password"
Conclusion
Qilin is now one of the most prominent ransomware threats globally. Its rapid rise, adoption by advanced threat actors, and the growing number of victims in late 2024 and early 2025 point to sustained activity well into the years ahead. The threat is likely to persist and potentially intensify, making preparation and prevention more critical than ever.
The ransomware family represents a significant evolution in cybercriminal sophistication, combining advanced technical capabilities with effective business operations to create a formidable threat.
Although Qilin follows a typical ransomware attack chain, its success lies in the effectiveness of its evasion strategies, allowing it to execute attacks with minimal detection until the final encryption phase.
The fight against Qilin ransomware is not just a technical challenge but also a strategic business imperative. Organizations that invest in comprehensive cybersecurity programs, maintain current threat intelligence, and prepare for incident response will be better positioned to resist this sophisticated threat and protect their critical assets and operations.
Sign up to use ANY.RUN’s TI Lookup for free: gather fresh actionable threat intelligence for quick detection and response.
Other malware & phishing threats
 IronChainIronChain is destructive ransomware and a wiper-like threat that uses elevated privileges, kernel-level components, security-control interference, and file encryption to disrupt Windows systems and potentially cause irreversible data loss.
 DarkSideDarkSide ransomware is a novel ransomware strain involved in high-profile incidents. Its attacks lead to data theft and encryption, causing significant damage to victims.
 LodaLoda is a remote access trojan (RAT) that has been in active use among multiple threat actors since 2016. The malware’s functionality includes stealing passwords and other sensitive information, keylogging, capturing screenshots, and delivering other malicious payloads. Loda is typically distributed as part of phishing email campaigns.
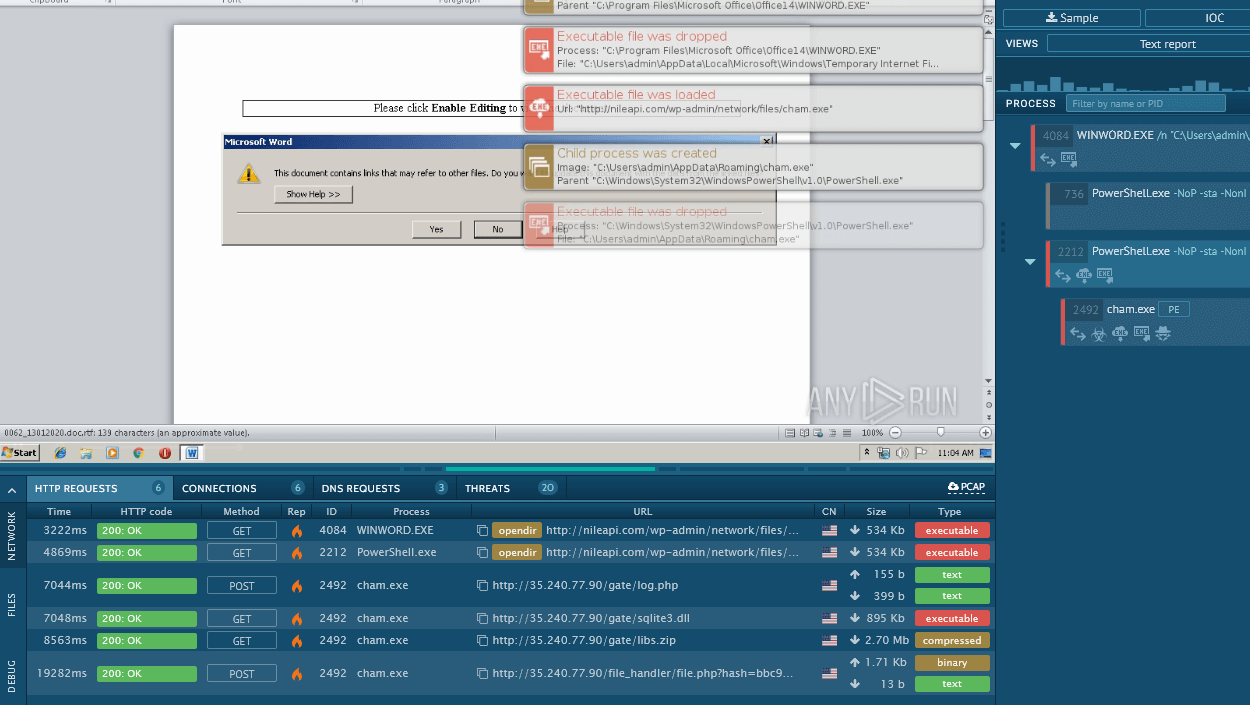 RaccoonRaccoon is an info stealer type malware available as a Malware as a Service. It can be obtained for a subscription and costs $200 per month. Raccoon malware has already infected over 100,000 devices and became one of the most mentioned viruses on the underground forums in 2019.
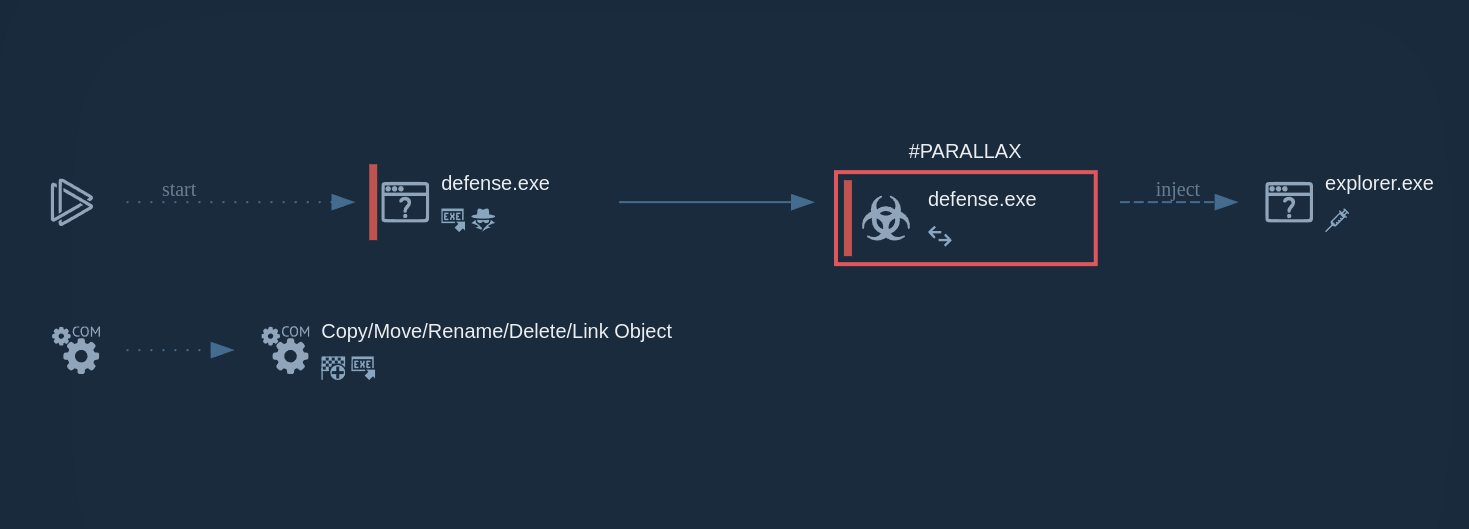 Parallax RATParallax RAT is a versatile malware capable of stealing credentials, recording keystrokes, capturing screenshots, and exfiltrating sensitive data. It hides under legitimate processes like Notepad, uses diverse communication channels, and establishes persistence to maintain control over infected machines.
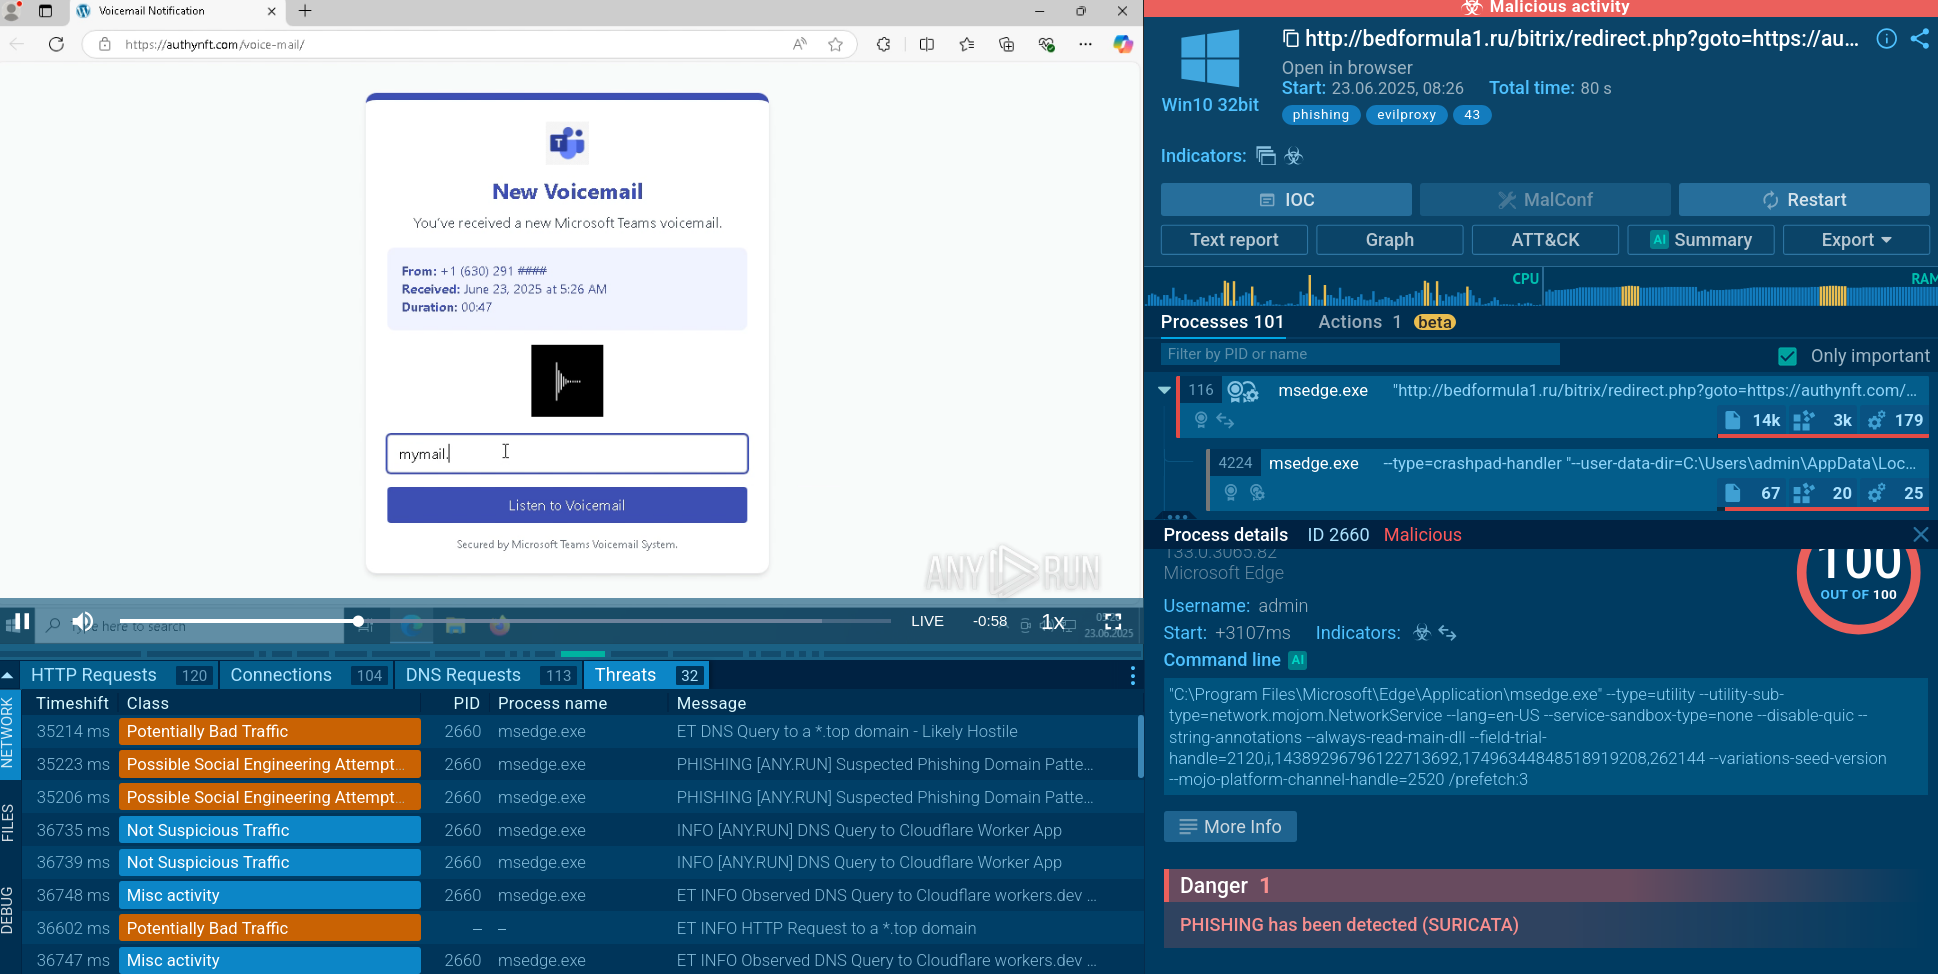 EvilProxyEvilProxy is a phishing-as-a-service (PhaaS) platform that enables cybercriminals to bypass multi-factor authentication (MFA) and hijack user sessions. It leverages reverse proxy techniques to harvest credentials and session cookies, posing a serious threat to both individuals and enterprises.